The Platform section controls settings that apply to the whole installation rather than to a single package: authentication, certificates, networking, the container registry, the storage license, replication, advanced options and the audit log.
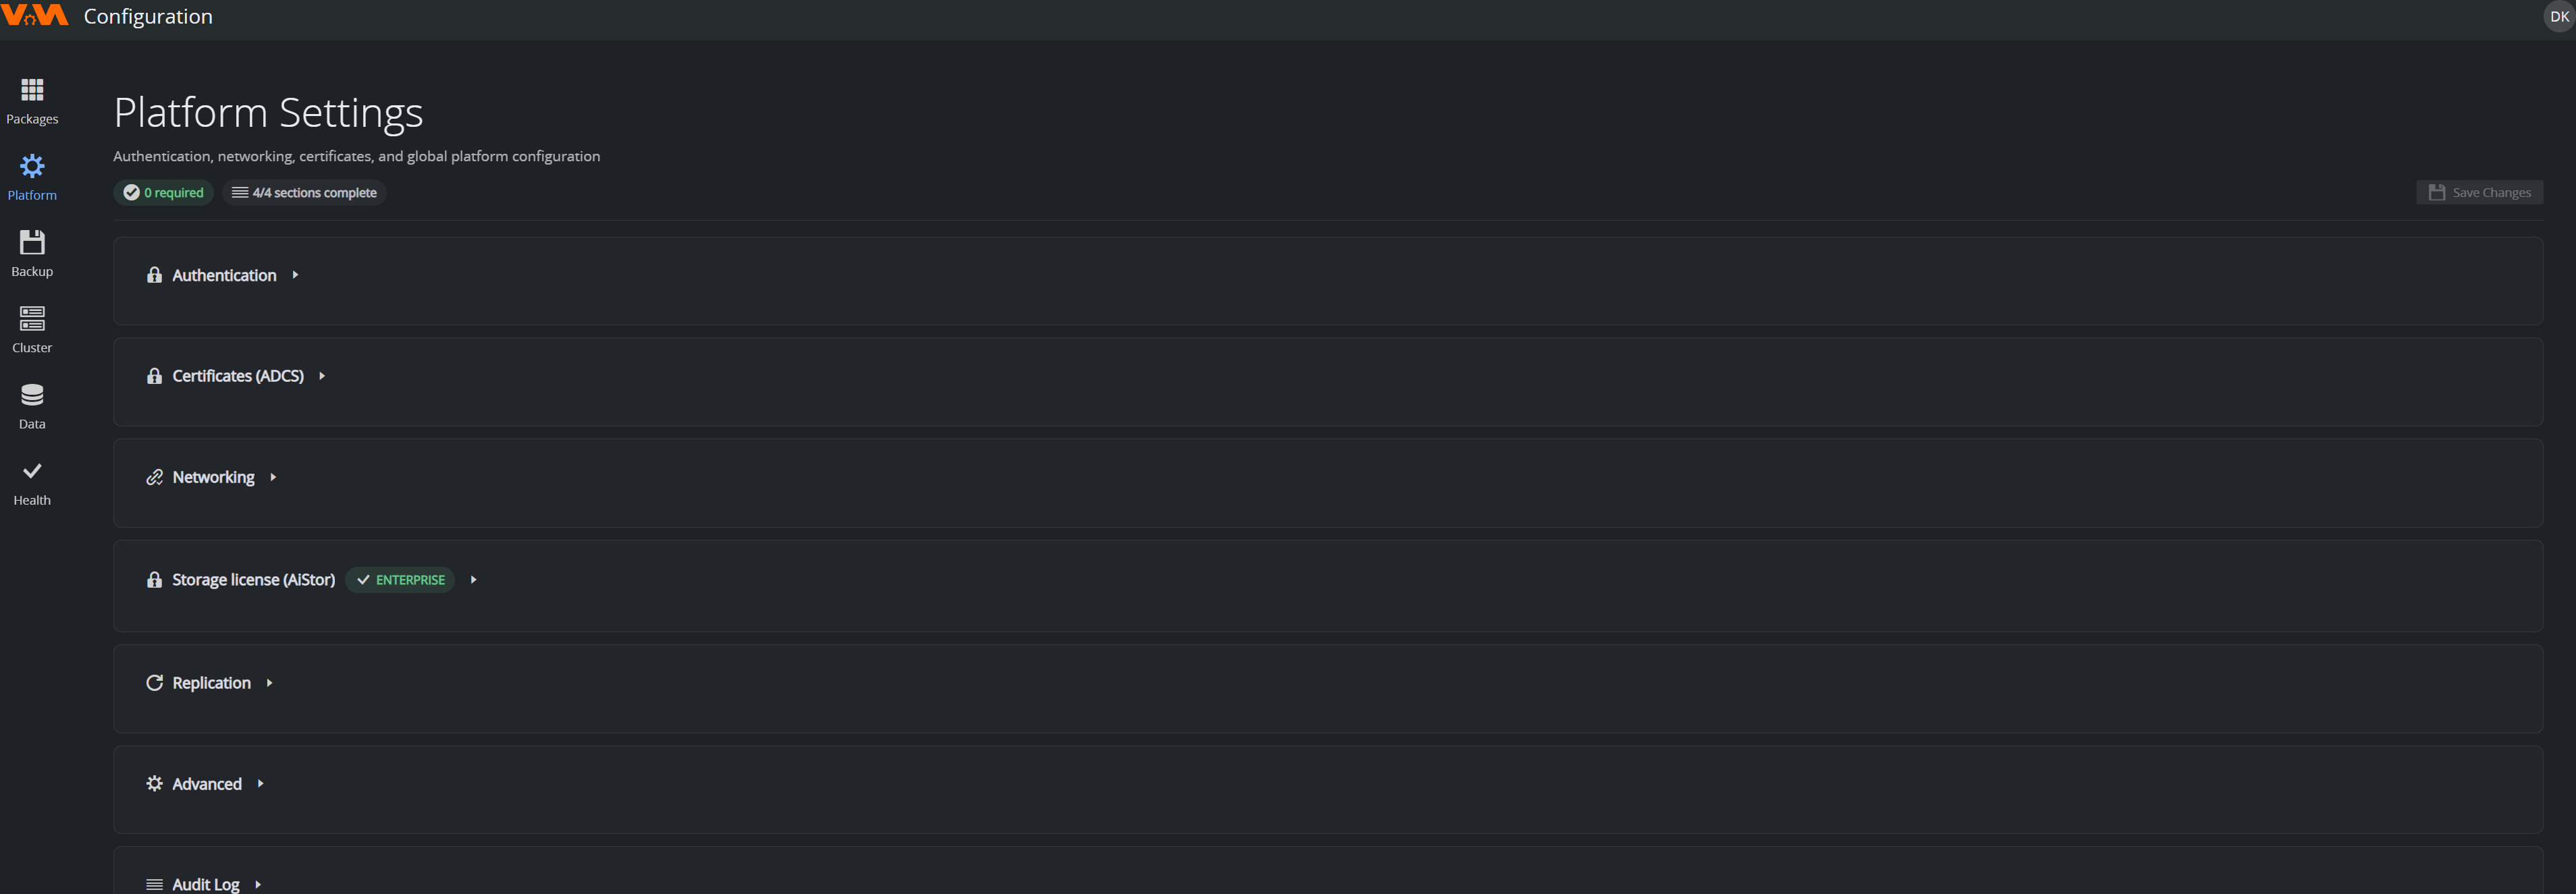
Platform settings are designed to be operable even when the VAM application itself is down. This is what makes recovery possible. You can sign in to the Configuration Service and fix platform settings even if VAM is reporting unhealthy.
Each area is a collapsible section. Open a section, edit its fields, then use Save Changes at the top-right.
Validate Before Apply, and the Safety Window
Platform changes are validated before they are applied, and risky changes have an undo window. This is what stops a typo from locking everyone out:
- Pre-flight validation: when you save, the change is checked against the live dependency first. A wrong or unreachable OIDC authority, or an unreachable ADCS endpoint, is rejected up front and nothing is written. A hostname that does not resolve in DNS yet causes a non-blocking warning, and the change still applies.
- Pending window and automatic revert: after an authentication or certificate change is applied, a banner asks you to confirm with Keep new settings. If you do not confirm within 5 minutes, for example because the change locked you out, the change reverts to the previous working values. You can also click Discard at once.
Authentication (OIDC)
Points every VAM service at your identity provider. The fields, the check on save and the steps for a new client ID or tenant are described in Identity Provider Setup > Changing the Provider After Install.
Certificates (ADCS)
How VAM obtains TLS certificates from your Active Directory Certificate Services authority. Fields: ADCS Server URL, ADCS Username, ADCS Password, Certificate Template and Issuer. The password is write-only: a Set or Not set chip shows whether one is stored. Leave the field empty to keep the stored password, or enter a new one to replace it.
A change to the URL, template, or credentials is canary-validated: the platform issues a throwaway certificate through a temporary copy of the issuer carrying the new values, and only if that succeeds does it update the live issuer and re-issue the affected certificates. A bad value leaves the running certificates untouched, and the banner tells you the validation failed.
- Restart affected services now: off by default. The new certificate is issued into its secret either way, so this toggle only controls whether the consuming services are restarted immediately (to present the new certificate) or pick it up on their next restart.
Networking
The external hostname and TLS settings clients use to reach the platform. On save, the hostname is checked in DNS. If it doesn't resolve yet you get a non-blocking warning (the change still applies) so you can add the DNS record afterwards.
Container Registry (Harbor)
The registry the platform pulls container images and Helm charts from. The section shows the Registry URL and the Username. To change the registry URL, user name or password, for example to rotate a robot account token, click Edit credentials. The change takes effect for the cluster immediately. Test connection checks that the platform can sign in to the registry.
Storage License (AIStor)
The enterprise object-storage (AIStor) license. The section header shows the current entitlement (for example, ENTERPRISE). To install or replace the license, click Update license, paste it into Paste the AIStor license blob and click Apply. To upload a license file instead, click Licensing at the top of the Platform page, click Update License and use the Upload file tab. Replication and other enterprise storage features are gated on a valid license.
This is the object-storage license only. VAM's own licensing is separate: it is served by a WIBU CodeMeter license server over the network, and there is no license file to install for it. See Prerequisites > Licensing.
Replication
Connect two clusters so they keep copies of each other's object data (active-active). You do one quick step on each cluster.
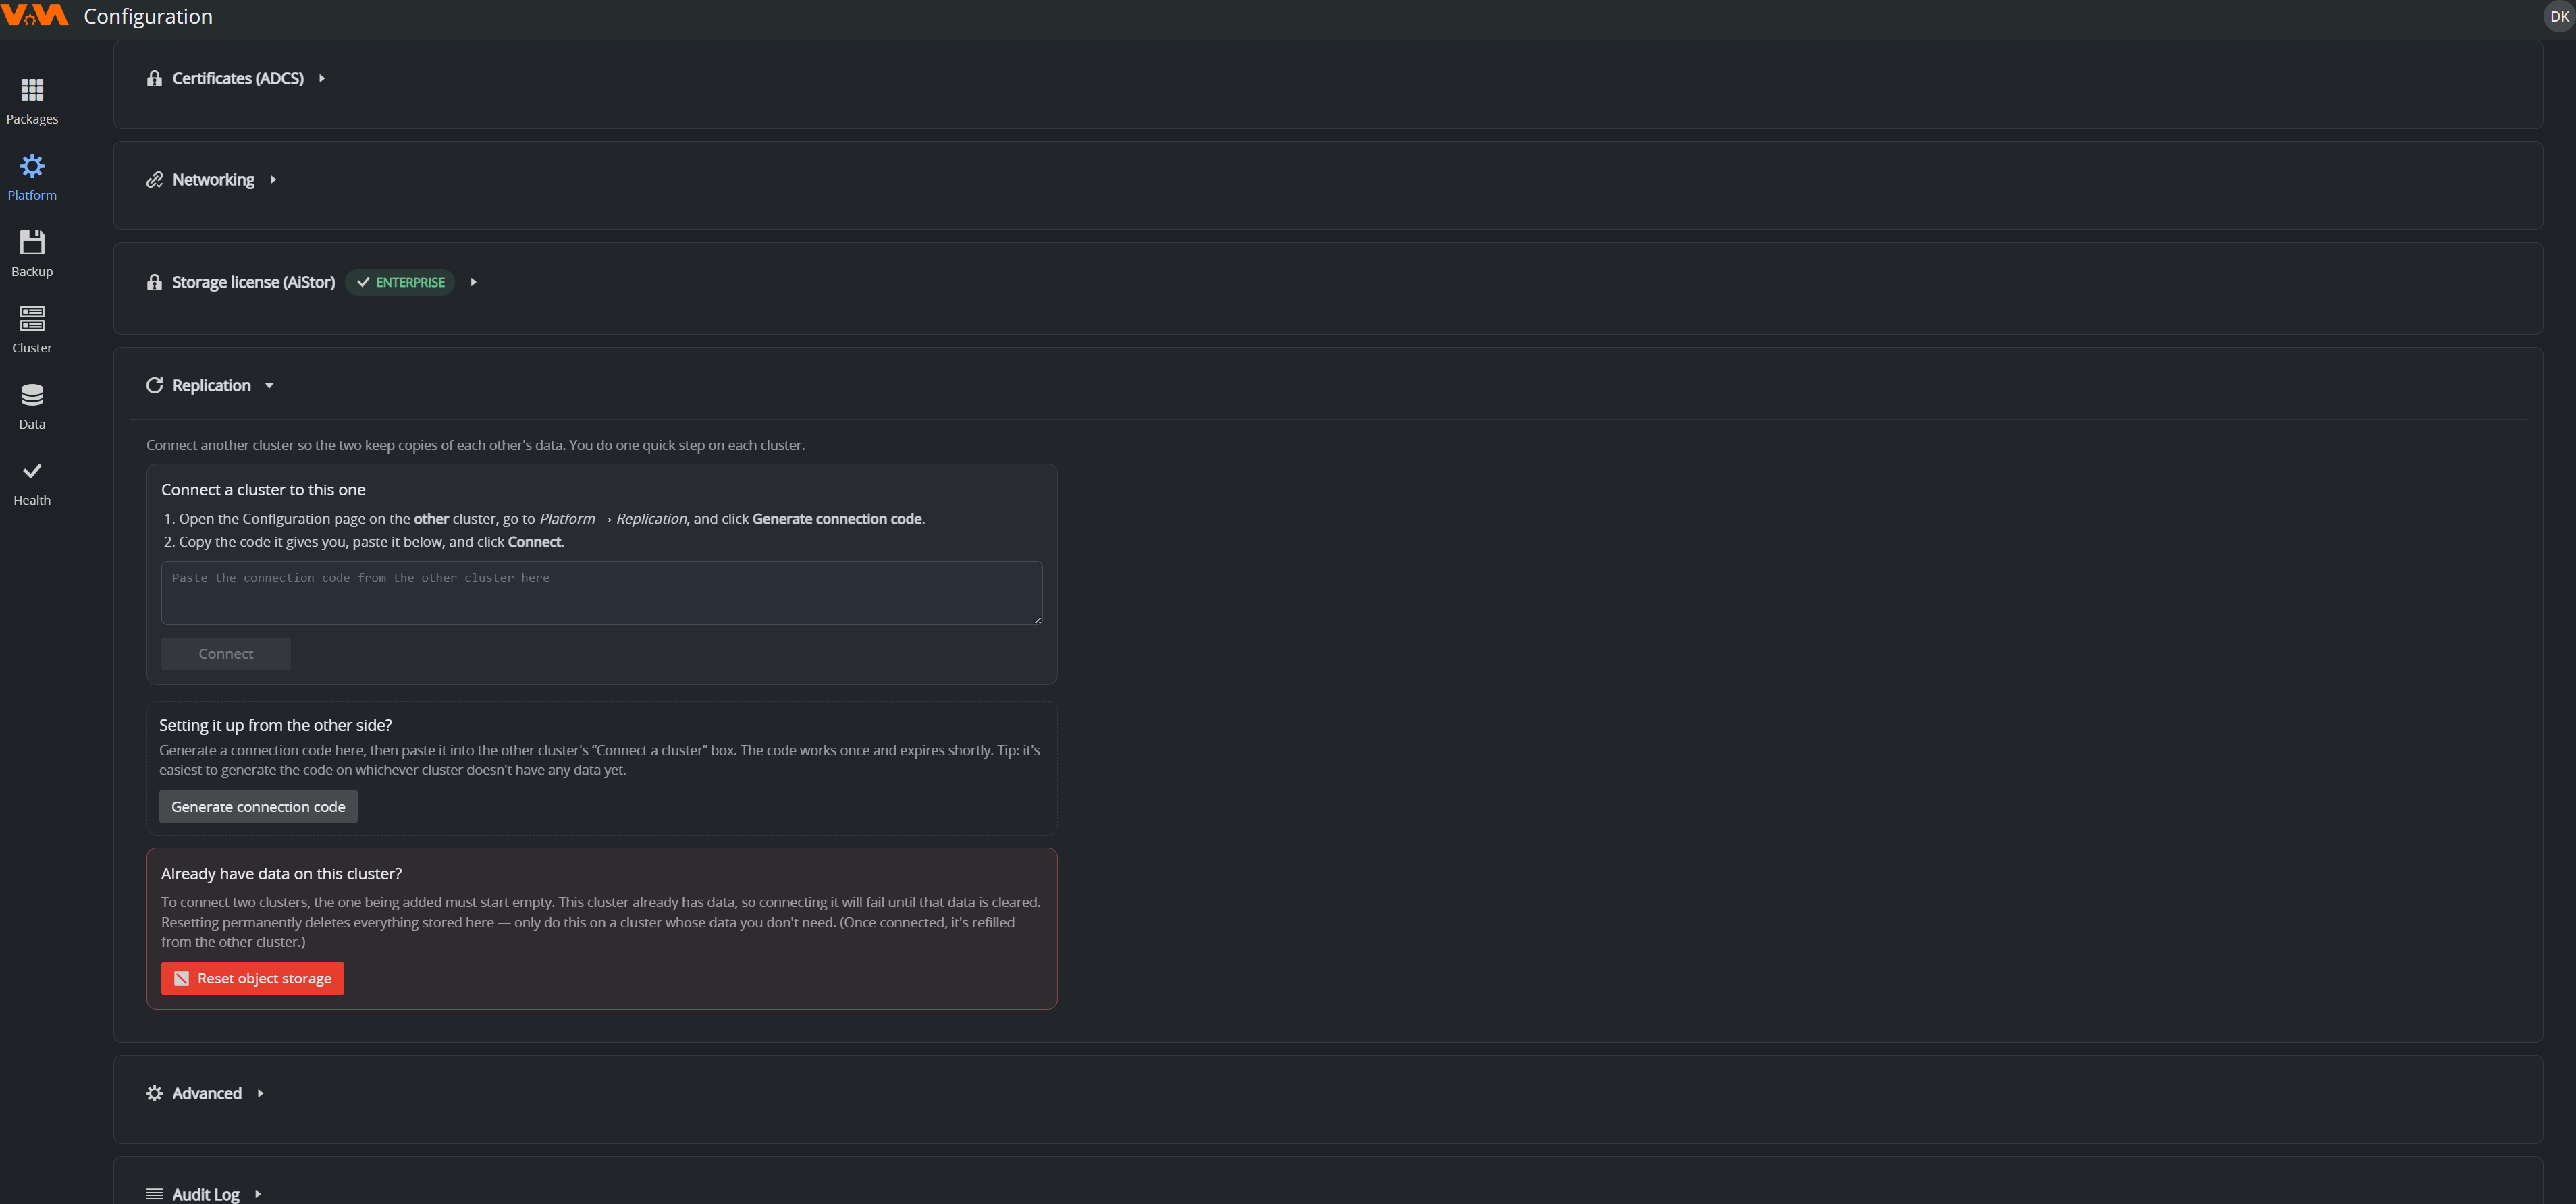
- On the cluster that does not have any data yet, open Platform > Replication and click Generate connection code.
- On the other cluster, paste that code into Connect a cluster to this one and click Connect.
The code is single-use and expires shortly. The cluster being added must start empty. The panel warns you and offers a reset if it already holds data. Once connected, the Replication view shows per-site status and an aggregate health summary. Disable replication removes all peer sites and tears down the mesh on this cluster.
Advanced
Less-common global options (for example developer-mode exposure of internal services). Most installations never need to change these.
Audit Log
A record of platform-configuration changes: who changed what, and when. Use it to review recent administrative activity.
Trust Roots
Admin-uploaded root CA certificates that the platform trusts (for example an internal CA that signs the ADCS endpoint or other services VAM calls). Reached from Platform > Trust Roots.
- Set the Restart workloads after applying changes switch first. It is off by default and decides whether running workloads are restarted now to pick up the new trust, or on their next restart. The upload or removal uses the switch as it is set at that moment.
- Click Upload PEM and choose a PEM-encoded root certificate.
- The root is added to the
vizam-trust-bundlethe platform distributes, and (best-effort) mirrored into the ADCS issuer's CA bundle.
Each root is listed with its subject, expiry and SHA-256, with a Delete action to remove it. A removal also follows the switch.
If the Configuration Service Does Not Start
There is a vamctl command-line path for emergency platform-settings recovery without the web UI. Contact Vizrt support.